Fortinet: The ASIC Bet in the Age of Cloud Security
I. Introduction & Episode Roadmap
There is a building in Sunnyvale, California, a few freeway exits from where the semiconductor industry was born, where engineers still do something most of the cybersecurity industry stopped doing two decades ago: they design their own chips.
Not chips in the marketing sense — not "purpose-built architecture" as a slide-deck phrase. Actual silicon. Tape-outs, mask sets, foundry relationships, the whole expensive, slow, unglamorous business of turning a networking function into transistors. In an industry that has spent the last ten years insisting that everything worth doing is delivered from the cloud as a subscription, Fortinet has kept a hardware engineering organization at the center of its identity, and it has been rewarded for it with roughly $7.5 billion of trailing-twelve-month revenue, gross margins near 80%, and one of the most profitable operating models in enterprise software or hardware.[^1]1
Here is the statistic that frames everything that follows. Fortinet ships more security appliance units than any company on earth — it has for years, by a wide margin. And yet, measured in dollars, it runs neck-and-neck with Palo Alto Networks, and in at least one quarterly snapshot, it actually trailed. Fortinet wins the count. Its rivals sometimes win the till. That gap between volume and value is not a footnote; it is the compressed version of the entire Fortinet investment debate, and it recurs in every section of this story.
The central question is this. Fortinet built an empire on custom silicon that made firewalls faster and cheaper than anything a general-purpose processor could deliver. That was a genuine, durable, hard-to-copy advantage — for roughly twenty years. But the growth vector in network security has moved to the cloud, to SASE and SSE architectures where security controls are delivered as a service from provider points-of-presence rather than from a box in a branch office. In that world, the question is not whether Fortinet's silicon is good. It is whether silicon matters at all. Does Fortinet have a second act? Or is it defending a hill that is slowly, quietly shrinking — and defending it extremely well?
The roadmap: how two brothers ran the same playbook three times; the founding wager on application-specific integrated circuits; the decade in which a firewall vendor tried to become a platform; the core business as it stands today and the one period when it visibly cracked; the cloud-security land grab and what Fortinet actually bought; the segment economics; the founders' capital allocation and credibility record; and then the most uncomfortable section of all — the fact that Fortinet's own products have been, repeatedly, the door through which nation-state actors walked into other people's networks. Then the frameworks, the bear and bull cases, and the small number of metrics that actually matter from here.
Start with the brothers.
 Subscribe on LinkedIn
II. Two Brothers, Two Exits, One More Company
The Fortinet origin story does not begin in a garage. It begins with a résumé that had already worked twice.
Ken Xie (谢青 Xie Qing) took engineering degrees from 清华大学 Tsinghua University — the institution that functions in China roughly the way MIT and Caltech jointly function in the United States — and then a master's from Stanford. His younger brother Michael Xie (谢华 Xie Hua) went a different route, to the University of Manitoba, and became the deeper systems engineer of the pair. Between them, they represented a specific and unusual combination in the security industry of the 1990s: people who understood packet processing at the silicon level and also understood how enterprises actually bought network gear.
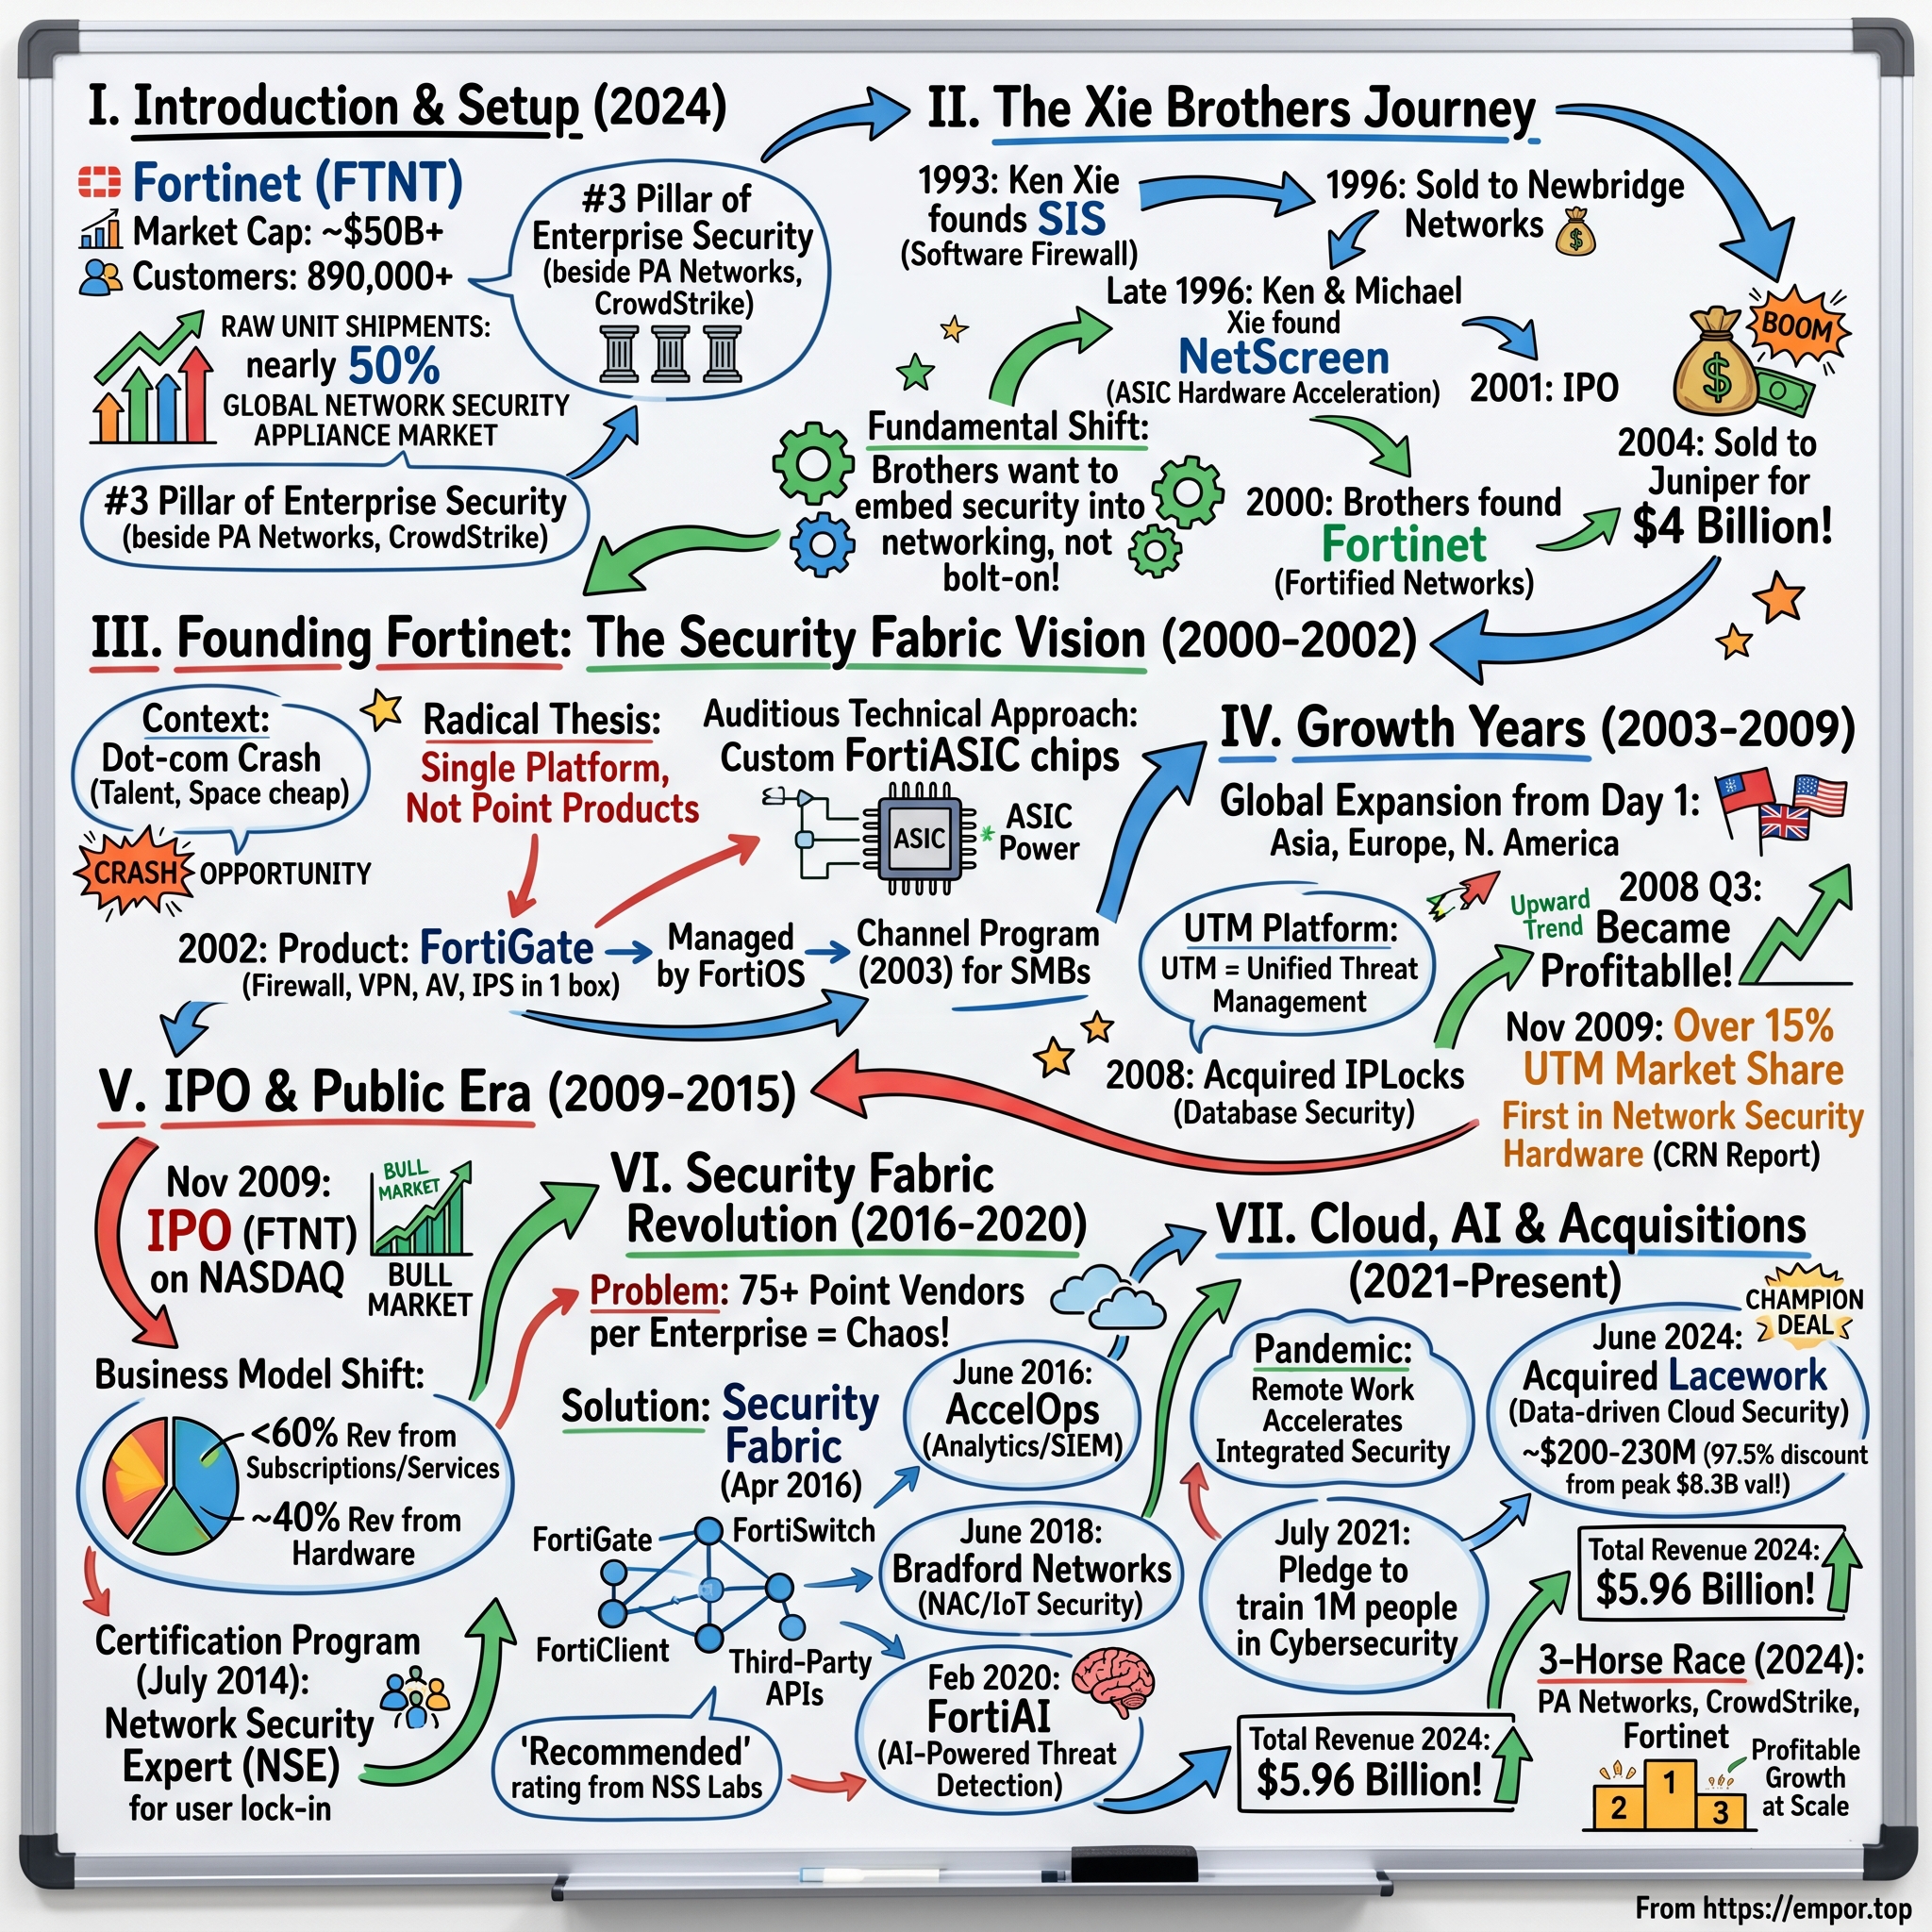
Ken's first venture, Systems Integration Solutions, launched in 1993, was the warm-up. The formative company was the second: NetScreen, founded in 1996, which did something the firewall industry considered either unnecessary or impossible depending on who you asked. It put firewall and VPN functions onto a custom ASIC.
To understand why that was radical, understand what a firewall was in 1996. It was software — Check Point's FireWall-1, most famously — running on a general-purpose server. Every packet that crossed the network boundary had to be inspected by a CPU designed to do everything, which meant it did nothing at maximum speed. Encryption in particular was brutal: VPN traffic could collapse a server's throughput by an order of magnitude. NetScreen's insight was that if you take the specific, repetitive, well-understood operations of packet inspection and cryptography and etch them directly into dedicated hardware, you get performance that a general-purpose CPU simply cannot reach at any comparable price. The analogy that holds up: a general-purpose CPU is a brilliant generalist employee who can do any task you give them; an ASIC is a machine on a factory floor that does exactly one task, ten times faster, and can never be retrained.
It worked. Juniper Networks acquired NetScreen in 2004 for approximately $4 billion — one of the largest security acquisitions of its era.
But Ken Xie had already left. In 2000, before that exit closed, he founded Fortinet.
This is the single most important thing to understand about Fortinet's founding, and it is frequently misread as visionary risk-taking. The ASIC-firewall playbook that built Fortinet was not an invention. It was a repeat. Ken Xie had built the first ASIC firewall company, watched it become valuable, and then set out to build a better version of it — this time with antivirus and intrusion prevention folded into the same box, and this time keeping control of the outcome rather than selling to a networking giant. Fortinet was a founder running his own play a second time, with the benefit of knowing exactly which parts had been hard.
That distinction matters for the investment case, because it changes what kind of advantage you think you are looking at. A one-time flash of insight is fragile. A repeatable institutional capability — designing security silicon, generation after generation — is something closer to what Hamilton Helmer calls process power: an advantage that accrues slowly, resists copying, and is embedded in an organization rather than in a person. Fortinet's twenty-six-year run of ASIC development is real process power. Whether process power in a category that is losing its growth is worth much is the question we will return to, repeatedly.
III. Founding Fortinet and the ASIC Wager (2000–2009)
The early 2000s were a bad time to start a hardware company. The dot-com collapse had drained venture capital out of anything requiring a fab relationship and an inventory line, and the enterprise security buyer was consolidating, not experimenting.
Fortinet's founding thesis was a bet that the buyer's real problem was not features but sprawl. A typical enterprise in 2001 ran a firewall from one vendor, an antivirus gateway from a second, an intrusion prevention system from a third, and a web filter from a fourth — four boxes, four management consoles, four support contracts, four upgrade cycles. Fortinet proposed collapsing all of it into a single appliance, a category that analysts would eventually name unified threat management. The pitch was not "our firewall is better than Check Point's." The pitch was "one box, one operating system, one price, and by the way it is faster because we built the silicon."
The economics of that pitch depended entirely on the silicon. Running four security functions in software on one commodity server produces a device that is slower than any of the four dedicated boxes it replaced — which is why nobody had successfully done it. Offloading the expensive operations to custom processors made consolidation possible without a performance penalty. That is the whole trick, and it is why Fortinet's hardware choice was not a manufacturing preference but the load-bearing wall of the product strategy.
The company raised roughly $13 million through 2003 — modest even by the standards of the time — and shipped the first FortiGate appliances in 2002. It built distribution the way hardware companies must: through a two-tier channel of distributors and resellers, aimed initially at the small and mid-sized businesses and branch offices that the enterprise-focused incumbents found unprofitable to serve. That channel strategy created the unit-volume position Fortinet still holds, and it also created the average-selling-price problem Fortinet still has. You do not get to pick one.
The period's major legal event was a patent suit from Trend Micro filed in 2004 over gateway antivirus technology, litigated in parallel at the International Trade Commission, and settled in 2006 for $15 million upfront plus ongoing royalties, with the broader matters winding down by 2010. It is worth naming and then moving past: an early, contained legal cost that constrained margins for a few years and never became a strategic wound.
Fortinet reached profitability in the third quarter of 2008 — a meaningful milestone for a hardware company eight years in, and an early signal of the cost discipline that would later define it. By 2009 it held the number-one position in UTM shipment share. In November 2009, it went public on NASDAQ, raising roughly $156 million at a valuation near $800 million.
For an investor reading this today, the 2009 IPO is mostly useful as a baseline. A company valued under a billion dollars at listing trades, seventeen years later, at a market capitalization around $126 billion. The compounding was extraordinary. The question the rest of this story asks is what generated it, and whether the generator still runs.
IV. From Firewall Vendor to Platform: Building the Security Fabric (2010–2020)
The 2010s were, for Fortinet, a decade of adding surface area.
The pattern established early was small technology tuck-ins rather than transformative acquisitions. Meru Networks, bought in 2015 for about $44 million, brought wireless access points. AccelOps, bought in 2016 for roughly $28 million plus an earnout, brought the security information and event management technology that became FortiSIEM. Neither deal moved the revenue needle on announcement. Both were bought for engineering and product, absorbed into the FortiOS ecosystem, and rebranded under the Forti- prefix.
That pattern — buy small, buy cheap, integrate into the single operating system — holds across nearly the entire company history, and it is the tell for how Fortinet thinks about growth. Most security companies of comparable scale bought their way into new categories. Fortinet mostly built, and when it bought, it bought components rather than franchises.
The architectural statement came in April 2016, when Fortinet announced the Security Fabric. Strip away the branding and the claim was specific: because every Fortinet product — firewall, switch, access point, sandbox, endpoint agent, cloud gateway — runs the same FortiOS and reports into the same management plane, a customer who deploys two Fortinet products gets something more than two products. They get correlation. A threat detected at the endpoint can automatically trigger a policy change at the firewall, which can quarantine a switch port, without a human writing integration code between three vendors' APIs.
This is the switching-cost claim, and it deserves to be taken seriously rather than dismissed as vendor-speak. In enterprise security, integration labor is the dominant hidden cost. A large organization running twenty security vendors is running twenty sets of alerts that do not talk to each other, and staffing an expensive team whose actual job is translating between them. A single-vendor fabric genuinely reduces that burden. Morningstar's wide-moat rating on Fortinet rests substantially on exactly this mechanism, alongside the silicon cost advantage.2
But note the shape of the claim, because we will test it twice more. The Security Fabric creates lock-in proportional to how many Fortinet products a customer deploys. For a customer running one FortiGate at a branch office, switching costs are trivial — that is a commodity purchase, competitively bid, and the buyer knows it. For a customer running FortiGate, FortiSwitch, FortiAP, FortiSASE, and FortiSIEM, switching means rebuilding an entire security architecture. The moat is real but it is not uniform; it is thin exactly where Fortinet has the most units and thick exactly where it has the fewest. And, as Section IX will show, concentration cuts both ways: a single vendor fabric means a single vulnerable operating system underneath everything.
Then came the pandemic.
From 2020 through 2022, every enterprise on earth simultaneously discovered that its remote-access infrastructure had been sized for a snow day, not for a permanent workforce dispersal. VPN concentrators buckled. Branch firewalls needed replacement. Budgets that had been scheduled for 2023 or 2024 were pulled into 2020 and 2021. Fortinet, sitting on the broadest hardware line in the industry with the best price-performance, had one of the great demand windfalls in security history.
Windfalls are wonderful. They are also, in the specific sense that matters to an investor, loans against future demand. Every firewall bought in 2021 because the office closed is a firewall not bought in 2024. Management would spend most of 2023 explaining this to a market that did not want to hear it — which is where the story turns.
V. The Core Business Today: Secure Networking, the ASIC Moat, and Its First Real Stress Test
On August 3, 2023, Fortinet reported second-quarter results and cut its full-year billings guidance. The stock fell roughly 24–25% in a single session, erasing tens of billions of dollars of market value in an afternoon.[^4]3
That day is the pivot of the modern Fortinet story, and everything in this section either leads to it or follows from it. But start with the thing being tested.
What the silicon actually does
Fortinet's appliances contain, alongside a conventional CPU, two families of proprietary processors: network processors that handle packet forwarding, policy enforcement, and VPN cryptography at line rate, and content processors that handle the deep inspection work — signature matching, antivirus scanning, decryption. The current generation includes the fifth-generation SP6 security processing unit, fabricated through Intel Foundry.
The performance claim Fortinet makes is a multiple of five to ten times better performance-per-dollar versus appliances built on general-purpose CPUs.2 The right way for a non-engineer to hold this: if a competitor needs a $40,000 server-class box to inspect encrypted traffic at a given throughput, Fortinet claims to do it in a box that costs a fraction of that. In a market where the buyer specifies throughput and then collects bids, a structural cost advantage of that magnitude is not a feature. It is a pricing weapon, and it is why Fortinet can win competitive deals at 40–55% off list price and still earn roughly 80% gross margins.
This is counter-positioning in the Helmer sense, and it is the cleanest example in enterprise security. Check Point, the software-first incumbent Fortinet was built to undercut, could not respond by matching Fortinet's price-performance without building its own silicon — which would have meant accepting hardware engineering costs, inventory, and a lower-margin business model that its own investors would have punished. The incumbent's rational choice was to not respond. That is the definition of counter-positioning: an advantage that persists precisely because copying it is against the incumbent's interests.
Where the volume-value gap shows up
And yet. Fortinet has led the industry in units shipped for years — cumulative FortiGate shipments passing 8.4 million, unit share exceeding 36% at points. But in IDC's fourth-quarter 2022 security appliance revenue snapshot, Palo Alto Networks recorded roughly $973 million, or 15.9% revenue share, narrowly ahead of Fortinet's roughly $967 million and 15.8%. Same market, same quarter: Fortinet shipped far more boxes and collected slightly fewer dollars.
The mechanism is not mysterious. Fortinet's strength is the branch office, the mid-market, the distributed retail chain with four hundred sites. Palo Alto and Cisco concentrate on the large-enterprise data center deal, where average selling prices are multiples higher and the buying committee weighs vision and roadmap more heavily than price-performance. Both are viable businesses. They are not the same business, and they do not command the same revenue per unit of engineering effort.
One small tell is worth naming because it reveals how the company itself weighs the critique: Fortinet's own marketing gradually shifted from leading with unit-share claims to leading with revenue-rank claims. Companies do not change their favorite statistic when the old one is winning the argument.
Gartner's first-ever Hybrid Mesh Firewall Magic Quadrant, published in 2026, sharpened the same point in a different register. Fortinet, Palo Alto Networks, and Check Point were named Leaders, and Fortinet ranked highest of all vendors on Ability to Execute for the second consecutive year — a direct validation of the operational and cost story.4 But on Completeness of Vision, Fortinet placed behind both Palo Alto and Cisco. And Gartner explicitly flagged "unexpectedly high total cost of ownership" at Fortinet as a named weakness — a genuinely awkward finding for a company whose entire founding thesis is price-performance. The likely reconciliation is that Fortinet's hardware is cheap and its licensing bundles, renewals, and add-on subscriptions are not; buyers who model the appliance price alone get surprised at year three. That is not fatal, but it does complicate the claim that the silicon advantage flows through to the customer's budget rather than to Fortinet's margin.
The stress test: 2022–2023
Now the disconfirming evidence, placed exactly where it belongs — next to the moat claim it tests.
The first tremor came in November 2022, when a softer outlook knocked the stock down about 11%. Management framed it as macro caution. Then came August 2023: with second-quarter results, Fortinet cut full-year billings guidance sharply, and the market's response was the 24–25% single-day decline noted above.[^4]3 Three months later, on November 2, 2023, the company cut billings guidance again, and the stock fell roughly another 23%.[^7] Across those two quarters, the peak-to-trough reset in full-year billings guidance was on the order of $700 million.
Read the management framing from those calls carefully, because it is the heart of the credibility question. The explanation offered was macro uncertainty, elongated deal cycles, and demand "normalizing to pre-pandemic levels." What management did not say was that competitors were taking share, and it did not directly characterize 2020–2022 as a pull-forward that the company had helped inflate by encouraging channel inventory build. The explanation was, in effect, "the weather changed."
Weigh this properly rather than merely reporting it. Two consecutive guidance cuts of that magnitude, three months apart, from a company that had just spent three years telling investors its demand was structurally driven by digital transformation, is exactly the pattern skeptics point to as evidence that the boom was inflated. A wide-moat business with genuine switching costs should not need to reset a year's billings outlook by hundreds of millions of dollars twice in a single year. The episode does not refute the moat claim, but it narrows it: the Security Fabric lock-in appears to protect retention of existing deployments far better than it protects the timing and volume of new hardware purchases, which turn out to be as cyclical as any capital-equipment business. That is a materially smaller moat than the one the 2021 narrative implied.
The partial vindication took about two years to arrive. Billings grew 31–33% year-over-year in the first and second quarters of 2026, and guidance was raised in consecutive quarters.[^8][^9] By that measure, management's "normalization, not share loss" framing was directionally correct — it simply took a two-to-three-year lag for results to confirm it, during which the market had no way to distinguish the honest version from the evasive one.
There was a smaller echo in 2025. Management disclosed that the 2023–2026 enterprise firewall refresh cycle — the replacement wave for all that end-of-support pandemic-era hardware — was roughly "40–50% through," which implied a smaller remaining tailwind than some investors had capitalized into their models. Shares fell double digits around several 2025 prints on that framing alone. This is worth flagging for a specific reason that recurs through this article: Fortinet's management has repeatedly been penalized for describing the boundaries of its own tailwind. That is, in isolation, a point in favor of their candor. It is also a reminder that a refresh cycle is by construction finite, and that any business whose growth is explained by one has an air pocket scheduled somewhere on the other side.
The seven-powers verdict on the ASIC bet
Here is the strategic core of the whole episode.
Fortinet's hardware-first architecture was a genuine counter-position against software-only incumbents for roughly two decades, and it produced process power — twenty-six years of accumulated silicon engineering that no security startup could replicate. Both powers are real. Neither is disputed.
But powers are not evaluated in a vacuum; they are evaluated against where the category's growth is going. And the same architecture that made Fortinet unbeatable against Check Point inverts into a liability against cloud-native rivals who never built an appliance business and therefore have nothing to defend. When security is delivered from a provider's cloud, the customer does not care what silicon is in the provider's data center — that is the provider's cost problem, not a product differentiator. Fortinet's ASIC advantage does not disappear in that world; it simply stops being visible to the buyer.
So the honest formulation is this: Fortinet possesses substantial process power in a category whose growth vector is flattening, and it is attempting to transfer that power into a category where its core mechanism does not obviously apply. That is not a broken company. It is a company whose most valuable asset is appreciating more slowly than the market it serves.
Which brings us to what Fortinet has done about it.
VI. The Cloud Security Land Grab: SASE, CNAPP, and What Fortinet Bought
In 2021, a cloud security company called Lacework raised $1.3 billion at an $8.3 billion valuation. It was, at that moment, one of the most valuable private security companies in the world, riding a category — cloud-native application protection — that investors believed would eat the entire security stack.
Three years later, Fortinet bought it for roughly $150 million.[^10]
That single fact contains both the best and the worst of Fortinet's cloud strategy, and this section unpacks both halves.
The SASE demotion
Start with the competitive scoreboard, because it moved in an unflattering direction at exactly the wrong time.
Secure Access Service Edge — SASE — is the architecture that merges networking and security into a cloud-delivered service. Instead of backhauling a remote worker's traffic to a corporate data center to pass through a firewall, you route it to the nearest point-of-presence operated by the security vendor, where policy is enforced in the cloud, and then out to the application. It is the single most consequential architectural shift in network security since the firewall itself, precisely because it removes the box from the critical path.
Fortinet was named a Leader in Gartner's 2025 SASE Platforms Magic Quadrant. In the 2026 edition, it was demoted to Challenger, while cloud-native pure-plays held or improved: Netskope led, Cato Networks leapt forward on its third consecutive year as a Leader, and Zscaler held Leader position.5 Notably, Palo Alto Networks also fell in that same 2026 assessment — this is not a Fortinet-only phenomenon, and any honest reading has to note that the appliance-heritage vendors moved together.
Still, the structural point stands: Gartner's own definition of SASE requires cloud-delivered controls, not appliance-anchored ones. Fortinet's architecture is a hybrid, and the company's "FortiGate-as-a-Service" bridge offering — essentially, running the FortiOS software you know on infrastructure someone else operates — implicitly concedes the mismatch.6 Bridge products are useful. They are also an admission that the two shores are different.
The competitive pressure is not hypothetical. Palo Alto Networks has claimed roughly 100 displacement wins worth more than $400 million in total contract value in its fiscal 2026, attributed to bundling SASE, firewall, and secure browser together. Displacement claims from a competitor's earnings call are marketing as much as measurement, and should be discounted accordingly. But the direction of the claim matters: the pitch that wins those deals is platform consolidation, which is Fortinet's own argument being run against it by a vendor with better analyst positioning in the growth category.
What Fortinet's own numbers say
Against all of that, Fortinet's disclosed SASE results have been strong in absolute terms. Unified SASE revenue surpassed a $2 billion run-rate, growing roughly 34% year-over-year in the second quarter of 2026.[^8] That is not the growth profile of a business being disrupted out of existence.
So the accurate finding is narrower and more interesting than "Fortinet is losing SASE." It is: Fortinet is losing the analyst-mindshare race in SASE while still compounding at better than 30% in absolute revenue. Those can both be true for a long time, because analyst quadrants lead procurement shortlists by years, not quarters. The falsification test is specific — if SASE growth decelerates toward the company average over the next four to six quarters while the pure-plays hold their rates, the quadrant demotion was an early warning. If SASE keeps growing at 30%-plus through 2027, the demotion was a definitional artifact of Gartner's cloud-delivery requirement rather than a demand signal.
CNAPP: honestly second-tier
Cloud-native application protection platforms — CNAPP — secure the workloads, containers, and configurations running inside AWS, Azure, and Google Cloud. It is a different skillset from network security, and Fortinet was late to it.
Analyst consensus across Wiz's own market surveys, KuppingerCole, and IDC MarketScape assessments consistently names Wiz, Palo Alto's Prisma Cloud, and CrowdStrike's Falcon Cloud Security as the top three by mindshare. Fortinet appears via Lacework, but not in that top tier. There is no way to write that sentence charitably, and it should not be written charitably.
The Lacework deal, benchmarked
Now the capital allocation verdict, which requires comparison.
Fortinet confirmed roughly $150–152 million for Lacework; Forrester's all-in estimate, including retention and integration costs, runs $200–230 million.7 Against Lacework's $8.3 billion 2021 peak, Fortinet paid on the order of 1–2% of the prior mark, at an implied revenue multiple somewhere between 1.7x and 3.3x.
Set that against the period's other cloud-security transactions. Cisco paid $28 billion for Splunk, announced September 2023 at $157 per share, roughly 7.8 times revenue.8 Palo Alto bought IBM's QRadar SaaS assets for about $1.1 billion. CrowdStrike bought Adaptive Shield for roughly $300 million. Check Point bought Perimeter 81 for $490 million. And the high-water mark of the entire cycle: Google's $32 billion agreement for Wiz, at something like 45 times annual recurring revenue.
By any of those yardsticks, Fortinet did not overpay. It bought a bubble casualty at fire-sale pricing, and the fact that there have been no disclosed goodwill impairments in the FY2022–2024 10-K filings is consistent with that.1
But the flip side is equally real, and treating the low price as unambiguously good is the error to avoid. The reason Lacework was available at 2% of its peak is that the cloud-security land grab had already happened — and Fortinet sat it out. From roughly 2020 through 2023, while Palo Alto and CrowdStrike were assembling cloud portfolios at prices that looked insane and buying the customer relationships and analyst positioning that came with them, Fortinet ran a materially weaker CNAPP offering. The discipline was genuine. So was the cost of the discipline: years of competitive absence in the category that every large enterprise was budgeting for. Cheap capital allocation and late strategic positioning are not opposites here. They are the same decision seen from two angles, and an investor should price both.
The Next DLP acquisition in 2024, at roughly $105 million, is the useful contrast case — a conventional small-cap data-loss-prevention tuck-in at a normal price, bought to fill a checkbox in the Unified SASE offering.[^15] Not every Fortinet deal is a distressed special situation; most are just ordinary component purchases.
The R&D tell
The deeper structural fact sits in the income statement. Fortinet runs research and development at roughly 12% of revenue. Palo Alto runs 21–27%. Zscaler runs 21–27%. CrowdStrike has run anywhere from 25% to far higher in its heavier investment years.
That gap is the single most revealing number in this article. It is simultaneously the explanation for Fortinet's superior margins — the profitability is partly a spending choice, not purely an efficiency achievement — and the explanation for why the company is a follower rather than a leader in every security category invented after 2015. Cumulative disclosed and estimated M&A spend across roughly eighteen years is well under $1.5 billion, against Palo Alto's more than $4 billion across seventeen deals in a comparable window. Fortinet has neither out-built nor out-bought its rivals in new categories. It has out-earned them, and returned the difference to shareholders.
Whether that is prudence or underinvestment depends entirely on whether the categories Fortinet skipped turn out to matter. So far the evidence is mixed: the CNAPP absence clearly cost position, while the decision not to pay 2021 prices for anything clearly saved billions.
One more honest note on execution risk. Several early Fortinet acquisitions — XDN/3Crowd, ZoneFox, OPAQ Networks — were quietly absorbed and their brands disappeared without ever becoming durable named product lines. No impairment was ever taken, because the deals were too small to require one. That is not a record of zero failures; it is a record of failures small enough not to leave a mark in the financial statements. The correct reading is that Fortinet's M&A discipline has protected it from catastrophic write-downs, not that every deal worked.
Sizing the optionality honestly
Fortinet's security-operations business — FortiSIEM, FortiSOAR, and the FortiAI products layered on top — reached roughly $490 million in annual recurring revenue, growing 21–25% year-over-year.[^8] Combined with the Lacework-derived CNAPP line, these represent genuine, fast-growing optionality for the platform thesis.
They also represent, together, a small minority of a roughly $7.5 billion revenue base. Treat them as what they are: real call options on Fortinet mattering in the next security era, not yet financially material to the investment case today. The conversion test is whether SecOps ARR compounds above 20% for another eight quarters without the core business subsidizing it through bundling giveaways.
VII. Business Model & Segment Economics
If Section VI was about strategy, this one is about the machine underneath it — and the machine is, by the standards of its industry, unusually well-built.
Fortinet reports three revenue lines. For fiscal 2025, product revenue — the appliances themselves — was $2.22 billion, about 32.6% of the total. Security subscriptions, the threat intelligence and service feeds that make the hardware useful, were $2.63 billion, or 38.7%. Technical support and other contributed $1.95 billion, or 28.6%.1
The number to extract from that is the recurring share: subscription plus support now represents roughly 67% of total revenue, up from around 60% in fiscal 2022. The business has been steadily converting itself from a hardware company that sells services into a services company that sells hardware.
Resist the temptation to call that shift permanent or structural, because it isn't entirely under management's control. The recurring share rises mechanically whenever hardware sales are weak and falls when a refresh cycle runs hot — which means part of the 2022-to-2025 mix improvement is the arithmetic of the post-pandemic hardware trough rather than a deliberate business-model transformation. Management's own disclosure that the current refresh cycle is roughly halfway through implies product revenue has more cyclical life in it, which would push the recurring percentage down even as absolute subscription dollars grow. Mix ratios in a two-speed business are a poor proxy for quality of revenue.
Geographically, Fortinet is the most balanced major US cybersecurity company. In fiscal 2025, EMEA at $2.83 billion was actually slightly larger than the Americas at $2.70 billion, with APAC at $1.26 billion.1 That balance is a legacy of the channel-first, mid-market strategy — European and Asian distributors picked up FortiGate precisely because it priced below the American enterprise incumbents. It cuts two ways for an investor: genuine diversification against any single region's IT spending cycle, and genuine exposure to European macro softness and currency translation that peers with 70% domestic revenue do not carry.
The margin structure is the headline. Gross margin runs near 80%; GAAP operating margin has run above 32% on a trailing basis; net margin near 28%.1[^8] For context, that is best-in-class among major cybersecurity pure-plays, several of which have historically run GAAP operating losses while growing faster. The correct attribution matters: Fortinet's profitability is not primarily financial engineering, and it is not primarily pricing premium — it is the combination of hardware cost advantage from the silicon and the structurally lower R&D intensity discussed above. Investors should hold both halves. The margin is real cash, and part of it is spending Fortinet chose not to do.
The services deceleration, and what management said about it
The most revealing thread across the last two years of earnings calls is not the headline beat. It is what analysts kept pressing on.
Service and SecOps billings growth decelerated for nine consecutive quarters before management stated, in the first quarter of 2026, that the trough had been reached.[^16] The important detail is the drift in the promise. On the third-quarter 2025 call, management framed the inflection as arriving in the second half of 2026. By the second quarter of 2026, the framing had become that the trough had already happened.[^8][^16]
That is worth naming rather than accepting at face value. A forecast that moves from "coming later this year" to "it already occurred" is not obviously a fulfilled forecast; it can also be a re-anchoring. The verification is arithmetic and will be visible within two or three prints: if service billings growth rates accelerate sequentially from here, the trough call was right. If they flatten at the trough level, management redefined the word.
The pressure on that point was real and public. On the third-quarter 2025 call, analysts from Oppenheimer, Deutsche Bank, and Citi pushed in sequence on product, SASE, and services deceleration — three separate firms circling the same question in one hour, which is usually a signal that the sell side has collectively decided the growth story needs defending.[^16]
To management's credit, the subsequent execution answered them. Each of the last four quarters — the third and fourth quarters of 2025 and the first and second of 2026 — delivered results above guidance accompanied by raised outlooks.[^17]9[^9][^8] That is a clean reversal of the 2023 miss pattern, and after the credibility damage of that year, four consecutive beat-and-raise quarters is the most meaningful evidence available that the guidance process has been rebuilt on conservative assumptions.
One open item flagged for the next print: on the second-quarter 2026 call, management explicitly declined to frame 2027, saying it was too early and that numbers would come in January or February.[^8] That is normal practice and not a red flag in itself. It is also the single most informative upcoming disclosure, because 2027 is the first year in which the refresh cycle tailwind is largely spent.
On pricing, management quantified a high-single-digit billings benefit from price increases taking effect in the second half of 2026, alongside list price hikes in the 5–20% range on selected products.[^8] That is evidence of real pricing leverage — but modest leverage, and partly a catch-up against input costs rather than pure margin expansion. It supports the claim that Fortinet is not being forced to discount its way to growth. It does not support a claim of pricing power comparable to, say, a monopoly infrastructure asset.
VIII. Current Management: The Xie Brothers' Capital Allocation and Credibility Record
Twenty-six years after founding the company together, Ken Xie remains Founder, Chairman, and Chief Executive Officer, and Michael Xie remains Founder, President, and Chief Technology Officer. There is no analogue to this in large-cap cybersecurity — no other company at this scale has been run continuously by the same two founding brothers since the first line of code.
That continuity is the source of both the best and the most concerning facts in this section.
Skin in the game
Per the 2026 proxy statement, Ken Xie beneficially owned approximately 9.8% of shares outstanding.10 Michael Xie's stake has been reported secondhand at roughly 5.5%, a figure that should be verified against the proxy's beneficial-ownership table directly before anyone relies on it. What is safely sayable: combined founder ownership sits meaningfully north of 10% of a company valued around $126 billion, which is a skin-in-the-game position measured in the billions of dollars per founder.
Ownership at that level changes incentives in ways compensation committees cannot replicate. It also concentrates governance risk, which is the trade every founder-controlled company makes.
How they are paid
The compensation structure is more rigorous than the founder-controlled archetype would predict. Annual cash bonuses are tied to revenue, billings, and operating income, with 2025 payouts scaling against 99–114% target achievement.10 Long-term equity comes as performance stock units vesting over four years, measured against Fortinet's total shareholder return relative to the S&P 500.
Relative TSR is a meaningfully harder bar than time-vesting restricted stock: it pays nothing for a rising market and pays for outperformance only. It is not a perfect instrument — TSR windows can be gamed by timing, and a four-year horizon in a capital-equipment cycle is short — but as founder-CEO pay structures go, this is toward the disciplined end.
Both founders sell shares exclusively under disclosed Rule 10b5-1 plans, adopted in 2023 and renewed in 2026.10 That is governance hygiene rather than a virtue, but the alternative — discretionary founder selling at a security company with irregular vulnerability disclosures — would be a genuine concern, so the absence is worth noting.
The capital allocation record
Fortinet's approach to capital is the most conservative in its peer group, and the most consistent over time.
Cumulative buybacks since 2016 have totaled roughly $8.4 billion, including $1.99 billion in 2022 and $2.29 billion in 2025, with the authorization raised to $10.25 billion running through February 2027.110 No dividend has ever been paid or planned. And the debt history is remarkable for what it does not contain: no convertible notes at any point in company history — an instrument nearly every high-growth technology company of this era used — and a single plain-vanilla $1 billion senior notes offering in 2021, split between $500 million at 1.00% due 2026, since repaid, and $500 million at 2.20% due 2031.1
The 2021 notes deserve a sentence of interpretation, because the timing tells you the motive. A company with Fortinet's cash generation did not need $1 billion in 2021. It issued at the bottom of the rate cycle because money was nearly free, and it issued in the simplest available form. That is opportunistic rather than necessitous financing, and the absence of converts means there has never been a dilution overhang hanging over the equity.
Put the pieces together and a consistent posture emerges: low R&D intensity, low M&A spend, high margins, and the residual returned through buybacks. This is not a growth-at-any-cost company wearing a profitability costume. It is, and has been for a decade, a cash-return company that happens to operate in a growth industry. Investors should decide whether they want that, rather than assuming the two profiles are interchangeable.
The activist stress test lands softly here for structural reasons. There is no evidence of any activist campaign in the past two years; 13D filings show none, and institutional holders appear as passive 13G filers. Founder ownership above 10% is itself a deterrent — a campaign that needs a proxy fight starts down double digits before it begins. Say-on-pay passed with approximately 88.7% approval at the June 2026 annual meeting.10 That is comfortable, and the roughly 11% dissent is above the level some governance advisors treat as worth noting, though well below anything resembling a revolt.
The credibility ledger
Here is the honest accounting on management quality, tested against the record rather than asserted.
In favor: twenty-six years of continuous operation, a demonstrated willingness to describe the limits of their own tailwind when it hurt the stock, a compensation structure tied to relative performance, a capital allocation record with no catastrophic deals and no dilutive financing, and four consecutive quarters of beating and raising after a credibility crisis.
Against: the 2023 sequence remains the main blemish, and it is a substantial one. Three quarters of macro-framed explanations that took roughly a year to be validated by results is a legitimate mark against guidance discipline, even granting that the explanation was eventually shown to be directionally correct. The lesson an investor should carry forward is not that management was dishonest — the subsequent data argues otherwise — but that Fortinet's forecasting process was not, in 2022 and 2023, capable of distinguishing a pulled-forward demand cycle from structural growth in its own business. That is a capability question, not an integrity question, and the four-quarter beat streak is the beginning of an answer, not the whole of one.
Then there is the gap that neither year of results addresses. No succession plan has been publicly disclosed for either founder. Both are in their sixties. They have run the company jointly for twenty-six years, and the CTO role in a company whose differentiation is custom silicon is not an easily replaced seat. This is a real governance gap, not proof of imminent risk — but in a company where more than 10% of the stock and essentially all of the strategic direction sit with two people, the absence of a named transition path is the kind of thing that is costless until the day it is not.
A minor related-party item belongs in the record for completeness: Fortinet has maintained a recurring legal-services arrangement with a firm where a board member's son is a partner, with payments historically ranging from roughly $400,000 to $7.2 million per year, reviewed by the Audit Committee.10 Disclosed, reviewed, and small relative to the company — worth naming, not worth alarm.
IX. The Products Are the Attack Surface: Security Incidents as a Live Moat Stress Test
In February 2024, the US Cybersecurity and Infrastructure Security Agency published an advisory that should be read by anyone who owns this stock. It described Chinese state-sponsored actors — the group publicly known as Volt Typhoon — pre-positioning themselves inside American critical infrastructure networks: energy, water, communications, transportation. Not stealing data. Waiting.11
One of the documented entry points was a Fortinet FortiGate firewall, compromised through CVE-2022-42475.11
Sit with the shape of that sentence. The device whose entire purpose is to be the boundary between a utility's control network and the internet was the thing that let the adversary in.
The pattern, not the incident
A single critical vulnerability proves nothing about a vendor. Every security company ships flaws; the industry's own products are written in the same imperfect languages as everything else. What matters analytically is cadence, severity, exploitation status, and whether the vendor or the attacker got there first.
On that basis, Fortinet's record across FortiOS, FortiProxy, and FortiManager is dense and sustained — roughly one to two major, remotely exploitable, CISA-catalogued incidents per year from 2022 through 2026.
CVE-2022-40684, an authentication bypass, was exploited before public disclosure. CVE-2022-41328 was attributed by Mandiant to the China-nexus group UNC3886, which had reverse-engineered FortiOS deeply enough to deploy custom implants and disable the device's own logging — meaning the compromised firewall not only failed to stop the intrusion but stopped recording it.12 In 2023 came "XORtigate," CVE-2023-27997, a heap overflow in the SSL-VPN interface serious enough that Fortinet published its own PSIRT analysis alongside clarifications about the Volt Typhoon campaign.13 CVE-2024-21762 was added to CISA's Known Exploited Vulnerabilities catalog the same day it was disclosed — that timing means active exploitation was already established at announcement. Later in 2024 came "FortiJump," CVE-2024-47575 in FortiManager, exploited by the group tracked as UNC5820 against more than fifty FortiManager instances before Fortinet's own advisory appeared. In 2025, CVE-2025-24472 was tied to an active ransomware campaign. In 2026, a credential-theft campaign nicknamed "FortiBleed" was linked to ransomware-as-a-service operators. And on January 28, 2026 — inside the current fiscal year — CISA published fresh guidance on ongoing exploitation of a new FortiOS authentication-bypass flaw, CVE-2026-24858.14
Weighing it against the moat
Now do the thing that most write-ups of this topic refuse to do: connect it to the thesis.
The Security Fabric argument from Section IV is that single-vendor consolidation reduces integration burden and creates switching costs. Both are true. But the same architecture means that a single flaw in FortiOS has blast radius across a customer's firewall, switch, access point, VPN, and management plane simultaneously. Concentration that produces operational efficiency in peacetime produces correlated exposure in wartime. A customer running five vendors patches five times a year for five different things; a customer running the Fortinet fabric patches once — and if they are slow, five product categories are open at once.
There is a second, subtler problem. Several of these incidents involved exploitation preceding Fortinet's own disclosure. For most software vendors that is embarrassing. For a company whose brand promise is that it detects threats other people miss, it is a direct contradiction of the product claim. And the repeated involvement of sophisticated nation-state groups — UNC3886, UNC5820, the Volt Typhoon cluster — indicates that FortiOS is not being probed opportunistically by commodity criminals. It is a priority target for the best-resourced attackers on earth, because Fortinet's market share makes a FortiOS zero-day one of the highest-leverage assets in offensive cyber.
So where does this leave the claim that Fortinet is a trusted security leader? Narrowed, not rejected. The commercial evidence is that customers have not left: revenue grew through every one of these incidents, and no disclosure to date has quantified customer attrition or financial impact attributable to any single vulnerability. Switching costs, it turns out, are stronger than security embarrassment — which is itself an important and slightly cynical finding about how enterprise security is actually bought. A trusted-vendor brand and a poor vulnerability track record can coexist indefinitely, because the buyer's realistic alternative is another large vendor with its own CVE list.
But "hasn't hurt yet" is not "cannot hurt." The unhedged version of the risk is a single catastrophic breach at a named, recognizable customer, traced publicly to a Fortinet zero-day, arriving in a news cycle where regulators are looking for someone to hold accountable. Nothing in the record to date says that is likely. Nothing in the record says the cadence of KEV-listed FortiOS and FortiManager vulnerabilities is slowing, either — the January 2026 advisory is the most recent data point, and it points the wrong way.
Track the cadence. It is a cheap, public, high-signal proxy for whether the engineering organization's security posture is improving.
X. Playbook: What the Fortinet Story Teaches About Durable Advantage
Step back from the ticker for a moment. Four transferable lessons come out of twenty-six years of this company.
Counter-positioning can invert. This is the big one. Fortinet's hardware-ASIC architecture was a textbook counter-position: an approach the software incumbent could not copy because copying it would have destroyed the incumbent's own margin structure. It worked for two decades. And then the category's growth moved to cloud delivery, and the exact same architecture became the thing weighing Fortinet down against rivals who never built appliances. The durability of a moat is not a property of the moat alone. It is a property of the moat relative to where the category's growth is pointing. A capability that is hard to replicate and no longer relevant is a museum piece with excellent margins. Investors who evaluate moats as static structural features — how hard is this to copy? — systematically miss this failure mode.
Capital discipline shows up in distressed buying, not in abstinence. Fortinet's Lacework purchase at a small fraction of the target's prior peak valuation is the case study in not paying bubble prices. But the honest version of the lesson includes the cost: discipline on price does not erase the multi-year competitive cost of having been absent from the category while it was being defined. The companies that overpaid in 2021 bought something real along with the dilution — position, customers, analyst standing. Fortinet bought the assets later and cheaper, and inherited a weaker starting line. Neither choice is obviously correct. Both should be priced.
A trusted brand and a poor security record are separate claims. This is the specific analytical error the cybersecurity sector invites. "Customers trust this vendor with their security" and "this vendor's products are secure" feel like the same statement and are empirically unrelated. Fortinet has demonstrated, over four consecutive years, that a vendor can carry a dense record of nation-state-exploited vulnerabilities and continue growing revenue, because switching costs, price-performance, and channel relationships dominate the purchase decision. Do not underwrite the brand and the product security as one variable.
Guidance credibility is earned back on a multi-year clock. Fortinet's 2023 explanation — that pandemic demand was normalizing, not that share was being lost — was eventually shown to be directionally right. It still took about two years of consistent beats before the market fully re-rated the company's forecasting. The asymmetry is worth internalizing: credibility is lost in one afternoon and rebuilt over eight quarters, and that gap is where the opportunity and the trap both live, depending on whether the explanation was true.
XI. Competitive & Strategic Position: Porter's Five Forces
Run the standard framework, but run it honestly rather than as a checklist.
Threat of substitution — high and rising. This is Fortinet's most acute force, and it is not a distant threat. Cloud-delivered SASE and SSE are structural substitutes for the appliance model, not merely alternative form factors. When a mid-market company with forty branches migrates to a cloud-delivered security service, it does not buy forty smaller firewalls; it buys zero. And Gartner's category definitions increasingly reward cloud-native delivery, which shapes procurement shortlists years in advance. Fortinet's counter is the hybrid mesh architecture — the argument that most enterprises will run both for a long time, which is very likely true. The question is whether "a long time" means a decade or a transition period.
Buyer power — moderate to high. Large enterprises multi-source security deliberately, as risk management and as negotiating leverage, and extract 40–55% off hardware list price in competitive situations. Fortinet's silicon cost advantage is what allows it to absorb that discounting at 80% gross margin — which reframes the ASIC story neatly. The chips do not primarily generate premium pricing. They generate survivable pricing under buyer pressure.
Supplier power — moderate. Custom silicon means foundry dependence; the fifth-generation SP6 is fabricated through Intel Foundry. That is a genuine concentration point, and one shared across the industry rather than unique to Fortinet. A foundry capacity shortage, a process node delay, or geopolitical disruption to advanced packaging would hit Fortinet's product line in a way it would not hit a pure-software competitor. This risk is structurally underweighted in most write-ups of the company because it has not yet bitten.
Threat of new entrants — high. Not in appliances, where manufacturing scale and channel depth are real barriers. But in the categories where growth is — cloud security, AI-driven detection — the barrier to entry is capital and talent, both of which have been abundant. Wiz is the archetype: a company founded in 2020 that reached a $32 billion exit without ever shipping hardware, ever building a distributor network, or ever employing a chip designer.
Rivalry intensity — very high and blurring. This is the defining feature of the current market. Every major vendor is platformizing into every other vendor's category at the same time. Firewall is a three-way fight between Palo Alto, Cisco, and Fortinet. SASE is five-plus vendors deep. CNAPP is six-plus. The consolidation argument — "buy everything from one vendor" — is now being made simultaneously by six vendors to the same customers, which means it is no longer a differentiator but a table stake, and the winner will be decided on execution and price rather than on the platform concept itself.
Net assessment: Fortinet occupies a defensible position in a category under structural substitution pressure, with a cost advantage that functions primarily as discount absorption rather than pricing premium, in a market where its historical differentiation has been commoditized into every competitor's pitch deck.
XII. Bear vs. Bull Case
The bear case
Cloud-native disruption is already scoring. The 2026 Gartner SASE demotion from Leader to Challenger is not a forecast of disruption; it is disruption showing up in the scorecard, one category over from the firewall stronghold. Analyst positioning shapes enterprise shortlists with a multi-year lag, which means the commercial consequences, if any, arrive after the rating does.
Demand durability is unproven across a full cycle. The 2023 guidance-cut sequence demonstrated that a wide-moat rating did not insulate Fortinet from a demand air pocket when a pandemic pull-forward unwound. Management has since disclosed the current refresh cycle is roughly half-spent. There is no structural reason the 2023 pattern could not repeat on the other side of it.
The product-security record undercuts the premium. A multi-year cadence of critical, nation-state-exploited vulnerabilities in flagship products is difficult to reconcile with a valuation near 17 times trailing sales and roughly 44 times trailing GAAP earnings — multiples that embed an assumption of trusted-leader status.
Succession is undisclosed. Two founders in their sixties, twenty-six years in, more than 10% of the stock between them, and no public transition plan.
Late and thin in cloud. Lacework was a bargain and also evidence of a missed window. Fortinet's CNAPP position is second-tier by every independent assessment, in the category with the most secular growth in security.
The bull case
Best-in-class profitability, honestly sourced. Roughly 80% gross margin and 32%-plus operating margin, generated by hardware cost advantage and lower R&D intensity rather than by financial engineering, one-time items, or aggressive capitalization. The cash is real and it recurs.
The switching costs are the credible part of the moat. For multi-product Security Fabric deployments, the cost of leaving is architectural rather than contractual — and the evidence that it holds is that revenue grew through four straight years of high-profile vulnerabilities that would have triggered churn in a low-switching-cost business.
Disciplined capital allocation with no hidden liabilities. Roughly $8.4 billion returned via buyback, no dividend commitment constraining flexibility, zero convertible-debt overhang, one small plain-vanilla bond, and no goodwill impairments. A boring balance sheet is an underrated asset in a sector where several peers have funded growth with dilution.
2026 execution has been strong on every disclosed metric. Four consecutive beat-and-raise quarters, billings up 31–33% year-over-year in the first half, SASE above $2 billion run-rate growing 34%, SecOps ARR near $490 million growing above 20%.[^9][^8] Losing a quadrant ranking while compounding a $2 billion business at 34% is a peculiar kind of losing.
Self-funding capacity for a catch-up. Fortinet generates enough cash to buy its way into cloud security without dilution, if it chooses to. The 2021-through-2023 abstinence was a choice, not a constraint — and the optionality to reverse that choice still exists.
Reconciling them
The bear and bull cases here are not arguing about the same variable, which is why they coexist so comfortably. The bull case is about the present-tense financial machine, and it is well-evidenced. The bear case is about the direction of the category five years out, and it is necessarily speculative. Nothing in the 2026 results refutes the bear case, because a business can compound at 30% right up until the architecture underneath it stops being what buyers specify.
The most defensible synthesis: Fortinet is an exceptionally profitable operator with genuine but narrowing structural advantages, currently executing well after a credibility setback, in a category where the growth vector is migrating away from its foundational differentiation faster than its financials yet reflect. The investment question is not whether Fortinet is a good business. It plainly is. It is whether the transition to cloud-delivered security happens slowly enough that Fortinet's cash generation and switching costs buy it enough time to arrive in the new category on its own terms.
XIII. Risk Radar & KPIs to Watch Going Forward
Three metrics carry most of the signal. Everything else is commentary.
First: Unified SASE and SecOps ARR growth rates, specifically whether the "services trough is behind us" claim from the second quarter of 2026 survives the next two to three quarters.[^8] This is the single highest-information disclosure Fortinet makes, because it tests two things at once — whether the cloud transition is converting, and whether management's forecasting process has actually been rebuilt. A sequential acceleration in service billings growth validates the trough call. A flat line at trough levels means the word was redefined.
Second: Gartner and IDC positioning shifts in SASE and CNAPP. Not because analyst rankings are truth, but because they are the leading indicator of enterprise shortlists. A recovery to Leader in the 2027 SASE quadrant would argue the 2026 demotion was a definitional artifact. A further slide, or a widening gap versus Netskope, Zscaler, and Cato Networks, would argue the cloud-native gap is structural and compounding.
Third: the frequency and severity of CISA KEV-listed FortiOS and FortiManager vulnerabilities. This is a free, public, unmanipulable proxy for whether the engineering organization's security posture is improving. The cadence has not yet broken.
On the risk side, four mechanisms are worth holding in mind, each with a specific transmission path rather than a generic label. Cloud-native substitution operates through procurement standards: as buyers standardize on cloud-delivered SSE, appliance refresh budgets get redirected rather than merely deferred. Demand cyclicality operates exactly as it did in 2023: a refresh air pocket on the far side of the current cycle produces a billings guidance reset, and the 2023 precedent establishes that the moat does not prevent it. Product-vulnerability risk operates through a single tail event — a KEV-listed zero-day tied publicly to a major breach at a recognizable customer, producing attrition that has never yet been observed but is entirely plausible given the incident cadence. And succession risk operates through concentration: the abrupt departure of either brother, in a founder-controlled company with no disclosed transition plan, would create both a strategic vacuum and a governance question at the same moment.
XIV. Recent Developments
As of September 22, 2026, the most recent reported quarter is the second quarter of fiscal 2026, announced July 29, 2026, which delivered results above guidance with the outlook raised — the fourth consecutive quarter of that pattern — alongside SASE revenue above a $2 billion run-rate growing 34% year-over-year and SecOps ARR near $490 million.[^8]
Four items sit open for the next update.
The first is whether management provides 2027 guidance at all, and on what assumptions. It was explicitly deferred on the second-quarter call with a pointer to January or February.[^8] Given that 2027 is the first year in which the enterprise firewall refresh tailwind is largely exhausted, the shape of that first 2027 frame is the most consequential forward disclosure on the calendar.
The second is Gartner and IDC repositioning in SASE and CNAPP, where the 2026 SASE assessment moved against Fortinet and the cloud-native pure-plays held their ground.5
The third is the vulnerability cadence. The January 28, 2026 CISA advisory on ongoing exploitation of a FortiOS authentication-bypass flaw is the most recent public data point, and it falls inside the current fiscal year.14
The fourth is a housekeeping item with governance relevance: Michael Xie's beneficial ownership percentage should be confirmed directly from the proxy's ownership table rather than from secondary reporting, since combined founder ownership is load-bearing for both the alignment argument and the activist-deterrence argument.10
References
-
Fortinet Annual Report on Form 10-K, FY2025 — U.S. Securities and Exchange Commission, 2026-02-25 ↩↩↩↩↩↩↩
-
Wide-Moat Fortinet Is at the Forefront of the Convergence of Networking and Security — Morningstar ↩↩
-
Fortinet Stock Plummets After Earnings — What Went Wrong — The Motley Fool, 2023-08-04 ↩↩
-
Fortinet, Palo Alto Networks top Gartner's Hybrid Mesh Firewall rankings — SDxCentral ↩
-
Gartner SASE 2026 rankings: Netskope leads, Cato Networks leaps, and Palo Alto Networks falls — SDxCentral ↩↩
-
Cisco to acquire Splunk for $157 a share in cash — CNBC, 2023-09-21 ↩
-
Fortinet Annual Report on Form 10-K, FY2025 — segment and guidance disclosures ↩
-
Fortinet DEF 14A Proxy Statement 2026 — U.S. Securities and Exchange Commission, 2026-04-28 ↩↩↩↩↩↩↩
-
CISA Advisory AA24-038A: PRC State-Sponsored Actors Compromise and Maintain Persistent Access to U.S. Critical Infrastructure — CISA, 2024-02-07 ↩↩
-
Chinese actors exploit FortiOS flaw — Google Cloud / Mandiant Threat Intelligence ↩
-
Analysis of CVE-2023-27997 and Clarifications on Volt Typhoon Campaign — Fortinet PSIRT Blog ↩
-
Fortinet Releases Guidance to Address Ongoing Exploitation of Authentication Bypass Vulnerability CVE-2026-24858 — CISA, 2026-01-28 ↩↩
 LinkedIn
 WhatsApp
 Reddit
 Hacker News
 Email
 Kindle
 RSS Feed
 Spotify
 Apple Podcasts
 Amazon Music
 Audible
 YouTube